PHP Warns of Another Unpatched RCE Risk Two Days After Emergency PHP2Shell Patch …

Что произошло: PHP has warned of another way an attacker could run code on a web server, two days after it shipped emergency fixes for the critical PHP2Shell flaws. The new issue, assigned CVE-2026-115560, affects only web applications configured in an unusual way, and PHP considers it an unlikely risk.The project is not issuing an emergency fix for it. Instead, it recommends turning off a feature called

(далее…)
Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge

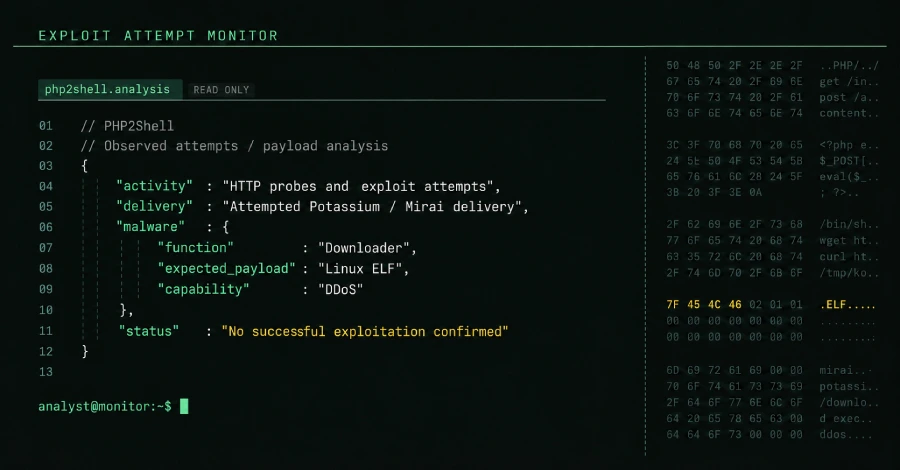
Что произошло: Researchers tie PHP2Shell attempts to a Mirai botnet and show an ASLR bypass, but no successful compromise has been confirmed yet. Two days after PHP rolled out emergency fixes for the PHP2Shell vulnerabilities, threat actors have tried to use the flaws to spread a Mirai botnet. A security firm has also built an exploit that gets past a key memory protection, and an exposed attacker server has revealed custom tooling. Even so, no successful in-the-wild compromise has been confirmed so far. The threat has prompted many organizations to take systems…

(далее…)

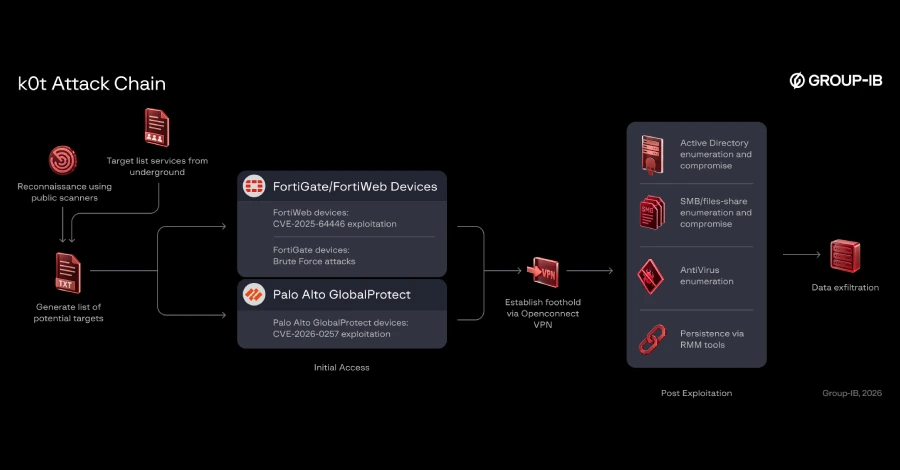
Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials

Что произошло: Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. "Artifacts from this investigation also indicate that operators in this campaign have obtained access to numerous organizations worldwide, and have attempted to further compromise some victims,

(далее…)

In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuil …

Что произошло: Noteworthy stories that might have slipped under the radar: Russia’s APT28 hit NATO defense firms, PingCAP source code stolen, ShinyHunters negotiator probe. SecurityWeek’s weekly cybersecurity news roundup offers a concise overview of important developments that may not receive full standalone coverage yet remain relevant to the broader threat landscape. This curated summary highlights key stories across vulnerability disclosures, emerging attack methods, policy updates, industry reports, and other noteworthy events to help readers stay well-informed about the evolving cybersecurity environment. Here are this week’s highlights: Heartbreaker macOS ransomware rebuilds itself from…

(далее…)

Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execu …

Что произошло: Cybersecurity researchers have discovered an artificial intelligence (AI)-driven intrusion ecosystem run by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an "Autonomous Red Team Kill Chain Framework" referred to as Phantom. The threat actor is assessed to be Russian-speaking and functions both as an intrusion and data-extortion operator, as well as an

(далее…)

PHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai Malware

Что произошло: Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges that weaponizing the flaws may be harder than previously thought. The attacks aim to exploit CVE-2026-109618 and CVE-2026-109619 (CVSS scores: 9.2), which can result in unauthenticated remote

(далее…)

© 2026 WorkServer.kz — ваш надежный IT-партнёр. Все права защищены.