Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaw …

Что произошло: Ruby has released versions 4.0.9, 3.4.12, and 3.3.13 to fix three bugs in Onigmo, the regular expression engine built into the language. The bugs lie behind four critical security flaws that GitLab patched over the past month. GitLab found that a specially crafted pattern could corrupt memory while Ruby compiles it, potentially leading to code execution on its own servers. Ruby says any

(далее…)
BlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing Revo …

Что произошло: Diplomatic organizations in Central Asia have been targeted by a sophisticated new Unified Extensible Firmware Interface (UEFI) bootkit called BlackX. The activity, which singled out diplomatic entities in Tajikistan, Uzbekistan, and Turkmenistan in early 2026, is suspected to be orchestrated by a China-linked state-sponsored hacking group known as APT41, Kaspersky said in a technical report

(далее…)

CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista …

Что произошло: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two vulnerabilities impacting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator (VCO) to its Known Exploited Vulnerabilities (KEV), citing reports of active exploitation in the wild. The critical-severity vulnerabilities are listed below - CVE-2026-110447 (CVSS score: 9.2) - An operating

(далее…)

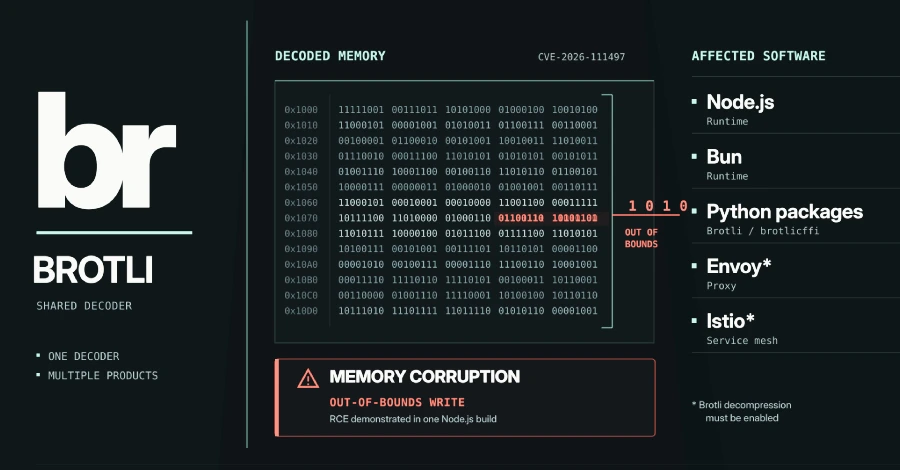
Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely …

Что произошло: A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli. Tracked as CVE-2026-111497, the flaw allows crafted compressed data to overwrite past the end of a buffer and corrupt a program's memory, potentially

(далее…)

Atlassian Patches 75 Flaws in Data Center and Server Products

Что произошло: Atlassian’s October bulletin lists 176 vulnerability entries, including 14 critical-severity issues, all in third-party components. Atlassian on Tuesday published its October 2026 security bulletin, which lists 162 high-severity and 14 critical-severity vulnerabilities. All of the entries are tied to third-party dependencies, and many CVEs appear under several products. By SecurityWeek’s count, the bulletin covers 75 unique CVEs, six of them rated critical. The affected products are Bamboo, Bitbucket, Confluence, Crowd, Fisheye/Crucible, Jira Software, and Jira Service Management. The critical-severity flaws are: CVE-2026-65637, CVE-2026-65182, and CVE-2026-68525 – Apache Tomcat issues listed…

(далее…)

Quest Diagnostics Data Breach Exposed ‘Certain Patient Records’

Что произошло: In a regulatory filing, Quest Diagnostics reported unauthorized access to its Quanum Lab Services Manager, a platform where certain clients can place test orders. Medical laboratory operator Quest Diagnostics said it learned of a cyber breach of one of its systems this week, likely compromising some records for patients. In a Thursday regulatory filing, Quest Diagnostics reported “unauthorized access” to its Quanum Lab Services Manager, a platform where certain clients can place test orders and receive or look up their results. The company said it discovered the hack on Wednesday…

(далее…)

© 2026 WorkServer.kz — ваш надежный IT-партнёр. Все права защищены.